

Policies Don’t Create Agility. Governance Does.
Organizations often respond to change by writing new policies.
The organizations that adapt fastest build governance systems that allow decisions to evolve without creating confusion.
IT Trends Weekly – Issue 043
Change Is Constant. Adaptation Is Not.
Organizations today operate in an environment where change is no longer an occasional disruption—it is a permanent operating condition. New technologies emerge continuously. Regulations evolve. Cyber threats mature. Economic conditions fluctuate. Customer expectations shift faster than strategic planning cycles.
Yet while change is constant, organizational adaptation often is not.
When faced with new challenges, many organizations instinctively reach for the same solution: write another policy.
A security incident occurs. A new policy is drafted.
A failed project triggers another approval process.
A compliance audit results in additional documentation.
An operational mistake produces another procedural requirement.
Each individual response appears reasonable. Collectively, however, they often create something far less beneficial: an organization that becomes progressively slower, more complex, and increasingly hesitant to make decisions.
Ironically, these organizations rarely become less agile because they lack capable employees or modern technology.
They become less agile because they unintentionally confuse documentation with governance.
This distinction has become increasingly important as modern governance frameworks evolve. The introduction of the GOVERN function in the National Institute of Standards and Technology NIST Cybersecurity Framework 2.0 reflects a broader recognition that governance is not simply about documenting expectations—it is about establishing how organizational decisions are made, monitored, and continuously improved.
Modern organizations are beginning to recognize a difficult truth.
Policies do not create organizational agility.
Governance does.
Governance defines who has authority to make decisions.
Governance establishes accountability.
Governance creates decision boundaries.
Governance enables organizations to change without losing consistency.
Policies remain important, but they are outputs of governance—not substitutes for it.
Perhaps the most useful way to understand this distinction is through a concept that deserves far more attention in executive leadership discussions.
We might call it Policy Debt.
Much like technical debt accumulates through shortcuts in software development, policy debt accumulates when organizations continually add documentation without modernizing the governance system that produced it.
The result is rarely improved control.
More often, it produces confusion, conflicting guidance, duplicated approvals, and slower organizational response.
Research examining bureaucracy across more than 7,000 organizations found respondents estimated that approximately 28 percent of their working time was consumed by bureaucratic activities, while nearly two-thirds believed bureaucracy slowed organizational decision-making.
Those numbers should concern every executive.
Not because bureaucracy exists.
Because much of it is self-created.
Organizations rarely design bureaucracy intentionally.
They build it gradually—one policy at a time.
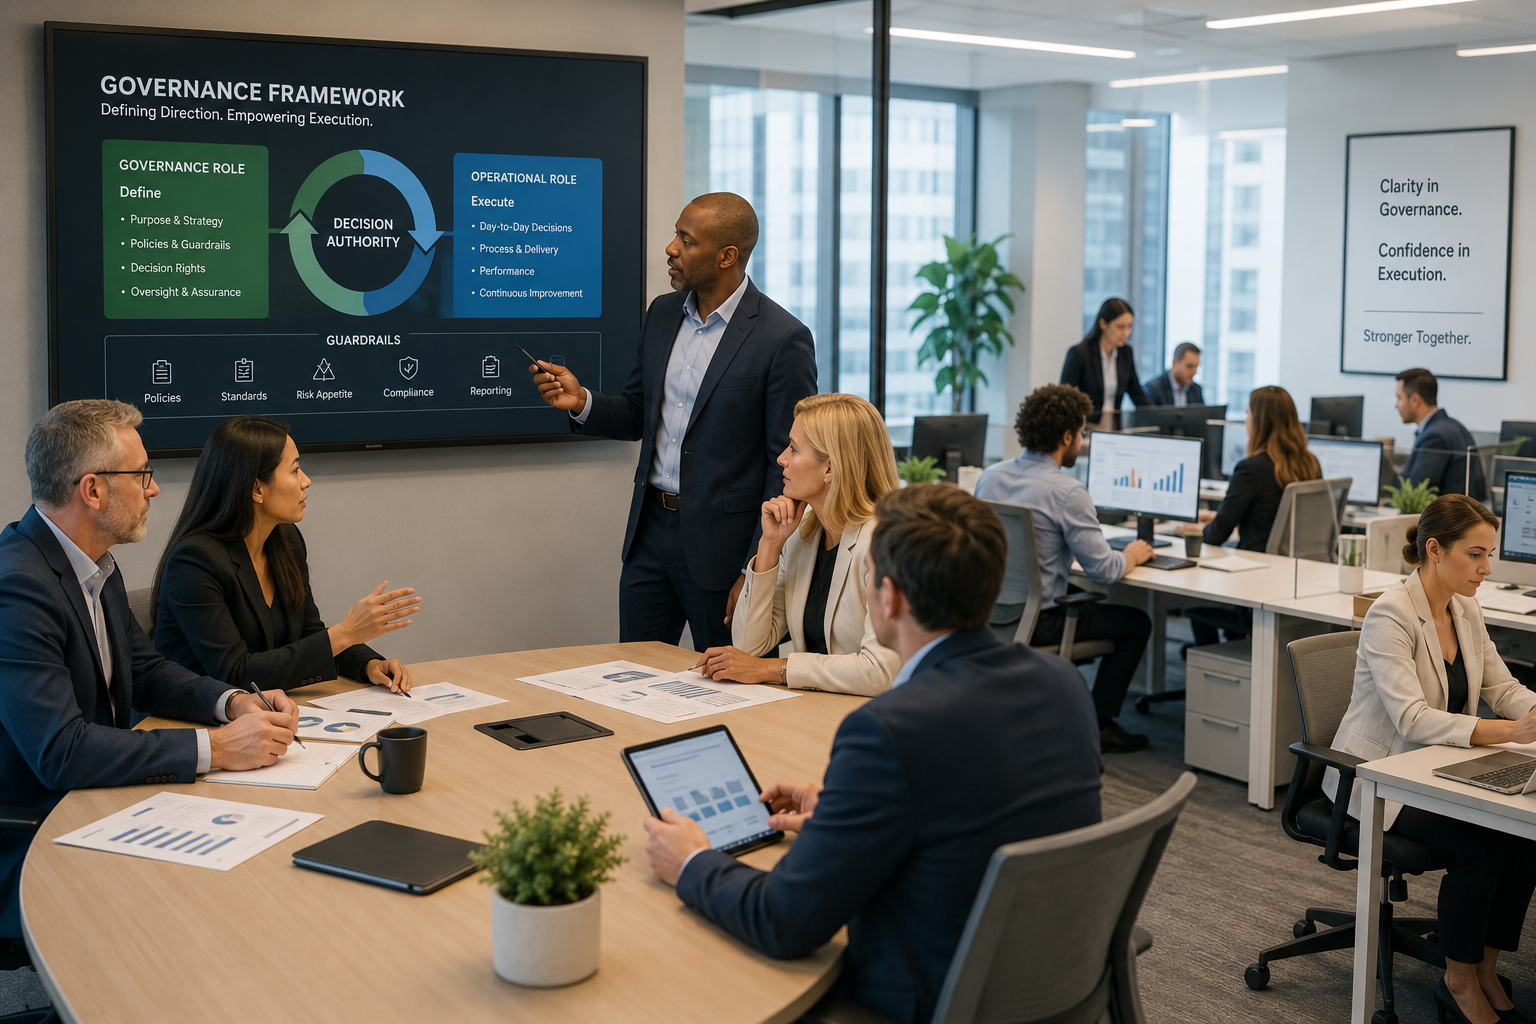
When Policies Become Technical Debt
Technology leaders already understand technical debt: small decisions made under pressure can eventually create larger maintenance problems later. Governance works the same way. When organizations respond to every issue by adding another policy, approval step, or procedural requirement, they may solve the immediate concern while making the overall system harder to operate.
That accumulation is what we can call Policy Debt.
Policy Debt is the growing collection of outdated, overlapping, redundant, or poorly governed policies that gradually reduces an organization’s ability to adapt. It does not usually appear as a single failure. It shows up as delay, hesitation, duplicated approvals, conflicting interpretations, and uncertainty about who has authority to act.
At first, the cost is hard to see. One additional approval requirement seems reasonable. A new exception form feels responsible. Another standard operating procedure appears harmless. But over time, the organization begins to carry more guidance than it can actively govern.
That is when policy stops creating clarity and starts creating friction.
The warning signs are familiar. Projects require additional approvals. Departments interpret the same policy differently. Teams hesitate to act without executive permission. Emergency decisions are forced through normal approval paths. Managers approve exceptions that never become lessons learned. Eventually, the organization begins asking the wrong question. Instead of asking how decisions should improve, it asks what new policy should be written.
The distinction matters because policies describe expected behavior, while governance determines how decisions evolve when circumstances change. Without governance, policies gradually drift away from operational reality. Employees compensate through informal workarounds. Operational knowledge moves from documented governance into tribal experience. Written guidance continues to expand, but confidence in that guidance declines.
The NIST Cybersecurity Framework 2.0 reinforces this distinction by placing governance around organizational context, risk strategy, roles, responsibilities, policy, oversight, and supply chain risk management. In other words, policy is only one part of a broader governance system. The framework does not treat policy as the goal; it treats policy as one artifact produced by governance.
Mature organizations manage policies through a lifecycle. They create them intentionally, review them regularly, measure them against current operational needs, update them when necessary, and retire them when they no longer serve the organization. Without that lifecycle, documentation naturally expands while organizational clarity contracts.
This is governance drift: the widening gap between written guidance and actual practice.
The hidden cost of policy debt is not paperwork. It is reduced confidence. When people are unsure which guidance is current, who can approve exceptions, or how decisions should change when conditions change, they slow down. They escalate. They wait.
And when enough people wait, the organization stops adapting.
Every organization accumulates policies over time.
Far fewer organizations periodically evaluate whether those policies still support the way decisions are actually made.
If approvals continue expanding, exceptions become routine, or employees hesitate because decision authority is unclear, the issue may not be compliance—it may be governance.
A periodic governance review can identify policy debt, clarify decision authority, and improve organizational agility without sacrificing accountability.
Whether your organization serves a municipality, a public agency, or a growing business, modern governance should help people make better decisions—not simply create more documentation.
Imperial Valley Info-Tech helps organizations modernize governance, strengthen operational resilience, and build decision frameworks that support confident, sustainable growth.
Governance Creates Decision Agility
If policy debt explains why organizations slow down, governance explains how they regain speed.
Agility is often misunderstood as the ability to move quickly or make decisions with minimal oversight. In reality, sustainable agility is rarely about removing structure. It is about designing governance that enables decisions to be made confidently by the right people, at the right time, within clearly understood boundaries.
This distinction is one of the most significant themes emerging from modern governance research. Organizations that consistently adapt to changing conditions do not rely on informal heroics or perpetual executive intervention. Instead, they establish decision rights, delegated authority, and accountability mechanisms that allow work to continue without unnecessary escalation. The result is not less governance—it is better governance.
One of the clearest examples of this philosophy appears in the MIT Sloan concept of “guardrails.” Rather than attempting to control every operational decision, effective governance establishes purpose, priorities, principles, and boundaries that define the space within which teams can operate independently. Employees gain the autonomy to respond quickly because the organization has already defined the conditions under which those decisions should be made.
This approach also aligns closely with the evolution of the NIST Cybersecurity Framework 2.0. By introducing GOVERN as the framework’s foundational function, NIST emphasizes that governance is responsible for establishing organizational context, assigning roles and responsibilities, defining risk strategy, and providing ongoing oversight. Those activities create the environment in which policies, standards, and operational procedures can remain relevant as the organization evolves.
Perhaps the simplest way to understand decision agility is to ask a single question:
Does your organization know who can make a decision before the decision becomes urgent?
If the answer is no, the organization does not have an agility problem. It has a governance problem.
Organizations with mature governance models rarely eliminate oversight. Instead, they move oversight to where it creates the most value. Executive leadership establishes strategic direction, acceptable risk, and organizational priorities. Managers operate within those boundaries. Frontline teams execute confidently because authority has already been defined rather than negotiated during every exception.
That clarity reduces delays, minimizes conflicting interpretations, and creates organizational confidence. People spend less time seeking permission and more time delivering outcomes. Governance becomes an accelerator rather than a bottleneck because it removes uncertainty from the decision-making process.
The goal of governance, therefore, is not to control every decision. It is to ensure that every decision can be made confidently by the right people at the right time.
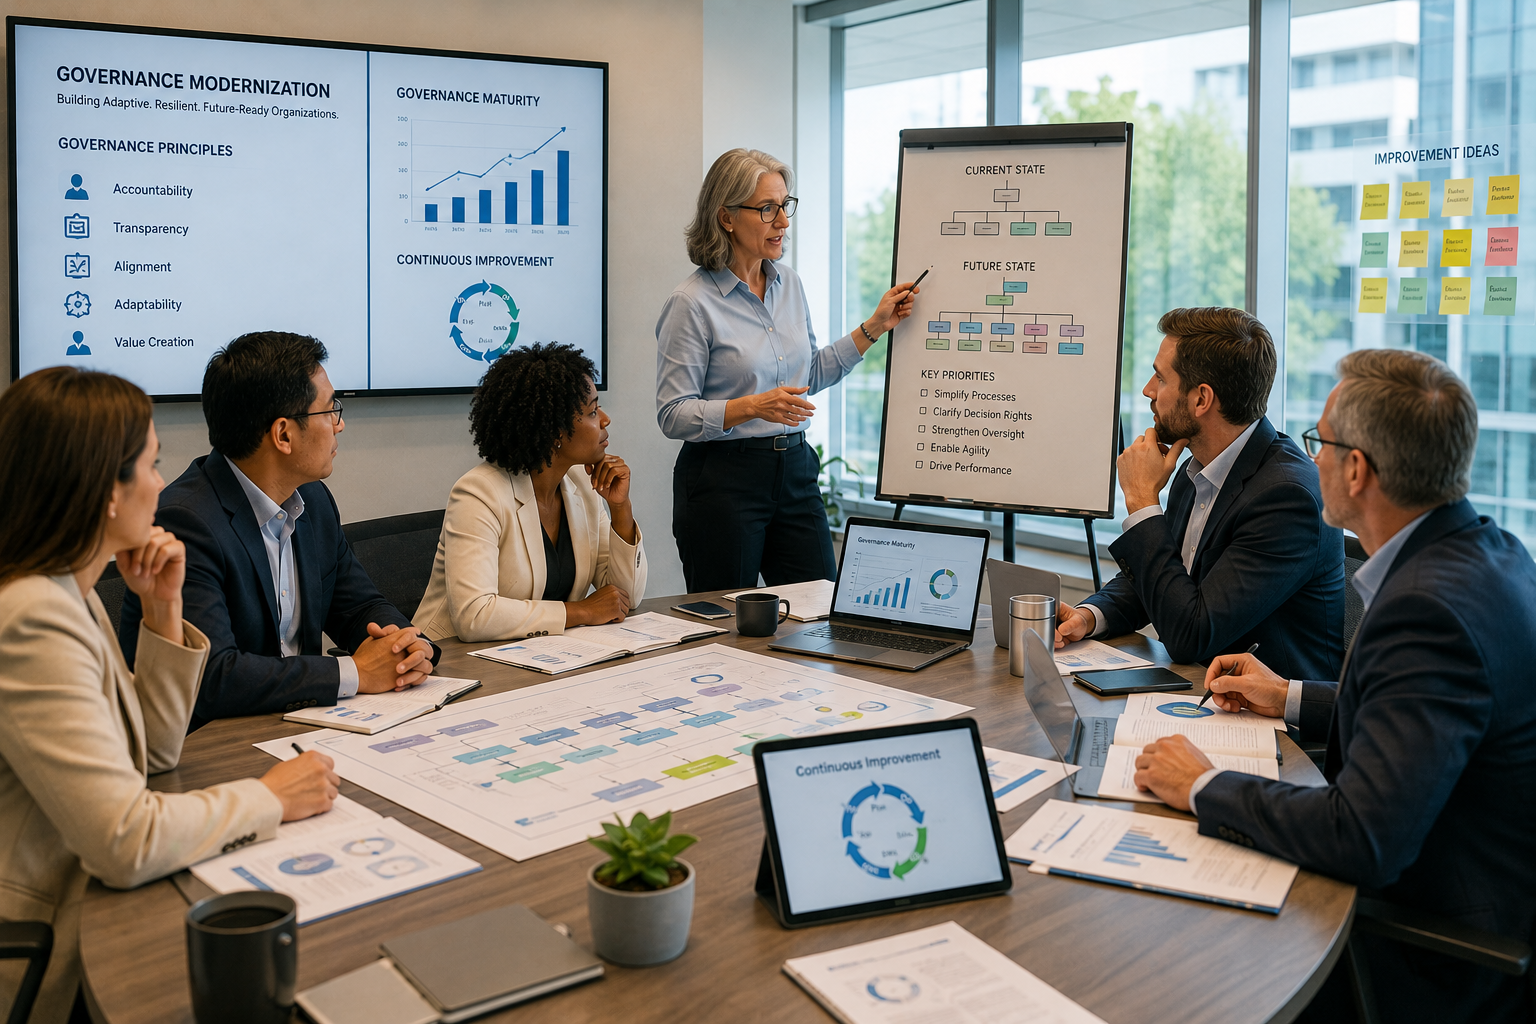
Change Without Chaos
One of the greatest misconceptions about governance is that modernization requires organizations to dismantle existing structures before they can become more adaptable.
The opposite is generally true.
Organizations that manage change successfully rarely abandon governance. They modernize it.
Governance modernization is not the process of writing new policies or creating additional oversight committees. It is the deliberate effort to ensure that governance evolves alongside the organization it serves. As technologies, business models, regulations, and risks change, governance must be capable of absorbing those changes without creating confusion or disrupting day-to-day operations.
This is where structured flexibility becomes essential. Mature organizations distinguish between principles that should remain stable and procedures that should evolve. Their governance establishes enduring expectations around accountability, ethics, risk tolerance, and decision authority while allowing operational processes to improve as new information becomes available.
The CISA Cyber Performance Goals reflect this same philosophy by encouraging organizations to integrate cybersecurity governance into everyday operations rather than treating it as a periodic compliance exercise. Governance becomes part of operational management, continuously refined through performance measurement, risk assessment, and executive oversight instead of isolated policy updates.
This perspective also changes how organizations think about change management. Rather than viewing every operational change as an exception that requires additional documentation, governance provides a repeatable framework for evaluating, approving, and implementing change consistently. The framework remains stable even as individual decisions evolve.
For smaller organizations, this principle is particularly important. Municipal governments, school districts, utilities, and growing businesses often lack dedicated governance teams. They cannot afford governance processes that depend on multiple committees or lengthy approval chains. Instead, they benefit most from governance models that clearly define authority, simplify escalation paths, and periodically review whether existing policies still support operational objectives.
Modernization, therefore, is not measured by the number of governance documents an organization publishes. It is measured by how confidently the organization adapts when circumstances change.
Enjoyed This Issue?
IT Trends Weekly is published every week for executives, technology leaders, municipal organizations, and business owners who want practical insights into governance, cybersecurity, AI, infrastructure, and the technologies shaping modern organizations.
Each issue delivers research-backed analysis—not headlines, hype, or vendor marketing.
Subscribe today to receive future issues directly in your inbox and stay informed about the trends, strategies, and governance practices that matter most to technology leadership.
Because better technology decisions begin with better information.
Adaptability Is Practiced
Organizations do not become adaptive simply because they declare adaptability to be a strategic objective.
Adaptability is developed through disciplined governance practices that continuously test assumptions, validate decision processes, and incorporate lessons learned into future operations.
This is why mature governance extends beyond policy management. It includes governance reviews, tabletop exercises, post-incident analysis, risk assessments, and continuous improvement activities that evaluate whether existing governance is still producing the desired outcomes. These activities are not compliance exercises; they are mechanisms for organizational learning.
Every significant operational event presents an opportunity to strengthen governance. A successful project can reveal decision structures worth repeating. An unsuccessful initiative may expose unclear authority, conflicting responsibilities, or outdated policies that require revision. In either case, governance improves because the organization deliberately converts experience into institutional knowledge.
This continuous learning cycle prevents governance drift. Instead of allowing policies and procedures to diverge from operational reality, organizations regularly compare documented expectations with actual practice. Gaps become visible, obsolete guidance is retired, and governance remains aligned with how the organization truly operates.
The organizations that adapt most effectively are not those that avoid mistakes. They are the ones that learn from them systematically. Governance provides the structure that transforms isolated experiences into repeatable organizational capability.
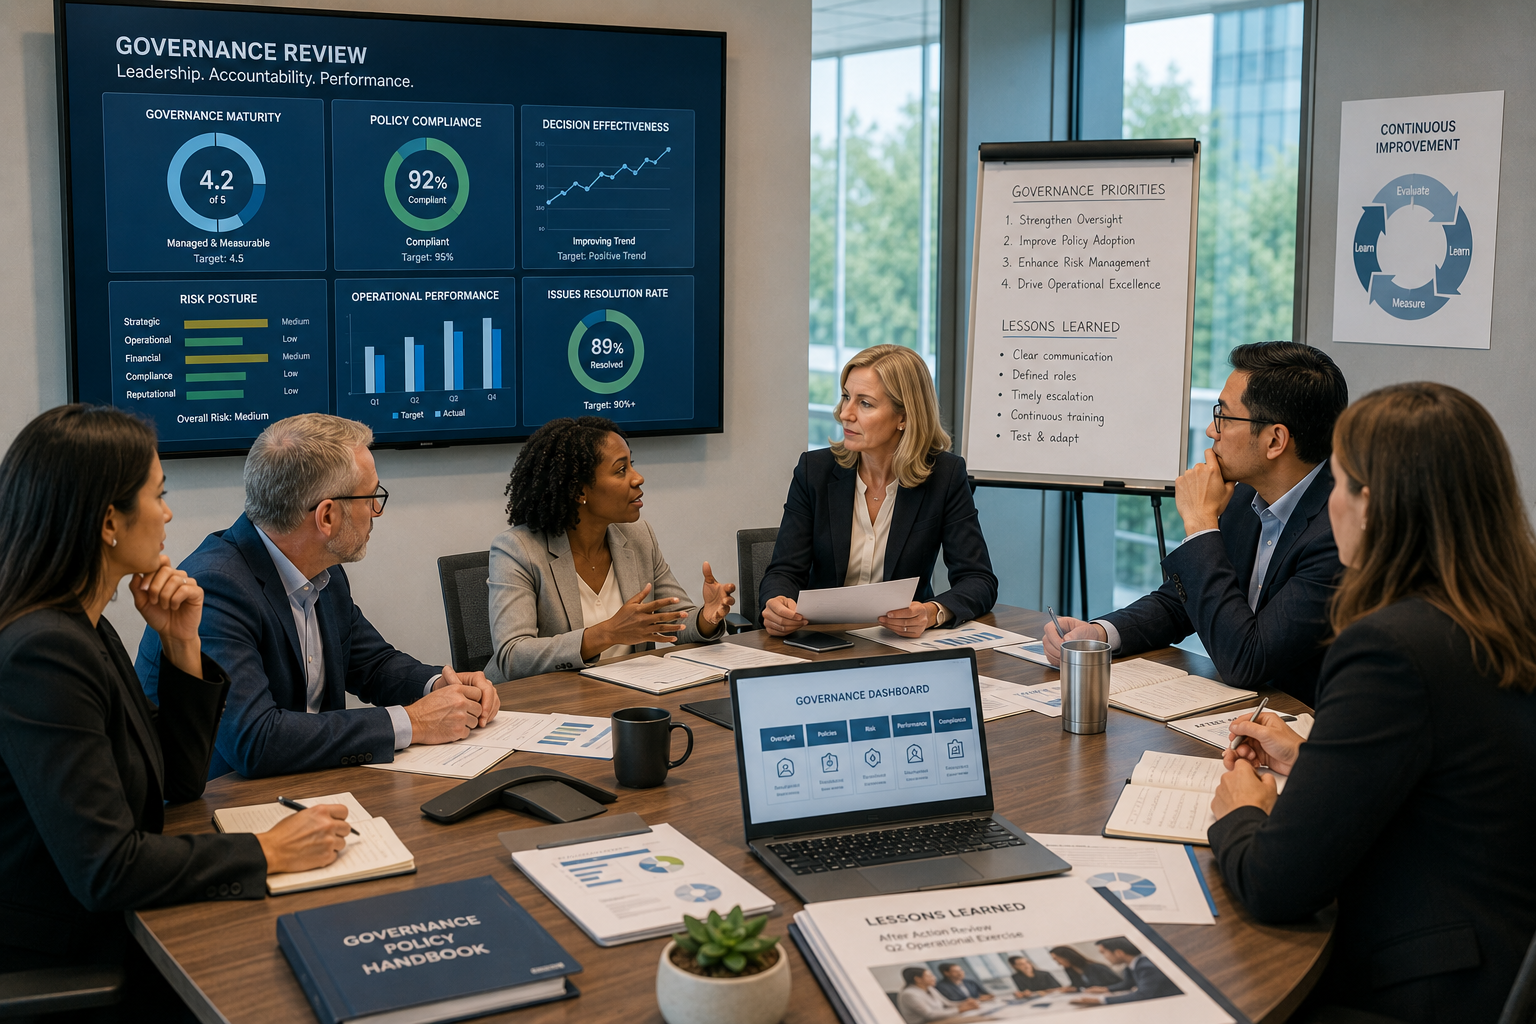
Organizations That Learn Faster Endure Longer
Competitive advantage has traditionally been associated with technology, financial resources, or market position. Increasingly, however, the distinguishing characteristic of resilient organizations is how quickly they learn.
Learning organizations do more than collect lessons. They incorporate those lessons into governance. Decision rights are clarified. Approval processes are simplified. Risk thresholds are adjusted. Policies are updated or retired. Governance evolves because leadership recognizes that yesterday’s decisions cannot govern tomorrow’s environment indefinitely.
This perspective fundamentally changes the role of governance. Rather than serving as a repository of historical decisions, governance becomes a living operating model that continually aligns people, processes, and technology with organizational objectives.
The introduction of governance as a foundational function within NIST CSF 2.0 reflects this broader evolution. Governance is no longer viewed as an administrative responsibility operating alongside the business. It is increasingly recognized as the mechanism through which organizations coordinate strategy, risk management, operational execution, and continuous improvement.
As emerging technologies such as artificial intelligence continue to influence decision-making, this capability will become even more important. Organizations will need governance systems capable of defining not only how people make decisions, but also how automated recommendations are evaluated, accepted, or challenged while maintaining clear human accountability.
The organizations that thrive over the next decade will not necessarily be those with the largest technology budgets or the most extensive policy libraries.
They will be the organizations that learn faster than their environment changes.
Closing Thought
Policies remain valuable. They communicate expectations, establish consistency, and document organizational decisions. Every mature organization needs them.
But policies alone have never created agility.
Governance does.
Governance defines who decides.
Policy records what was decided.
When organizations confuse those two concepts, they gradually accumulate policy debt, slow decision-making, and create unnecessary organizational friction. When they distinguish between them, governance becomes an operating capability that enables confident adaptation rather than bureaucratic control.
Policies describe what organizations intended to do yesterday.
Governance determines how they adapt tomorrow.
The organizations that thrive are not those with the most policies.
They are the ones with the confidence—and the governance—to evolve them without losing direction.
Sources & References
The research and analysis presented in this issue were informed by the following authoritative publications and frameworks:
- National Institute of Standards and Technology (NIST) – Cybersecurity Framework (CSF) 2.0, including the GOVERN Function
https://www.nist.gov/cyberframework - NIST Cybersecurity Framework 2.0 (Official Publication PDF)
https://nvlpubs.nist.gov/nistpubs/CSWP/NIST.CSWP.29.pdf - Cybersecurity and Infrastructure Security Agency (CISA) – Cross-Sector Cybersecurity Performance Goals (CPGs) Version 2.0
https://www.cisa.gov/cross-sector-cybersecurity-performance-goals - Harvard Business Review – What We Learned About Bureaucracy From 7,000 HBR Readers
https://hbr.org/2017/08/what-we-learned-about-bureaucracy-from-7000-hbr-readers - MIT Sloan Management Review – The Four Guardrails That Enable Agility
https://sloanreview.mit.edu/article/the-four-guardrails-that-enable-agility/ - MIT Sloan Management Review – Scaling AI with Adaptive Governance
https://sloanreview.mit.edu/article/scaling-ai-with-adaptive-governance/ - MIT Sloan Management Review – The Great Power Shift: How Intelligent Choice Architectures Rewrite Decision Rights
https://sloanreview.mit.edu/article/the-great-power-shift-how-intelligent-choice-architectures-rewrite-decision-rights/ - U.S. Government Accountability Office (GAO) – Results-Oriented Cultures: Implementation Steps to Assist Mergers and Organizational Transformations
https://www.gao.gov/products/gao-03-669 - Microsoft Learn – Integrate NIST CSF 2.0 Governance into the Secure Future Initiative
https://learn.microsoft.com/security/zero-trust/sfi/integrate-nist-2-governance - IBM Think – Understanding NIST Cybersecurity Framework 2.0
https://www.ibm.com/think/insights/nist-cybersecurity-framework-2
Disclaimer
Editorial Note
IT Trends Weekly synthesizes publicly available research, recognized industry frameworks, and professional experience to provide practical guidance for executive leadership. Source material is reviewed and analyzed independently to develop original editorial perspectives intended to support informed decision-making.
Copyright
© 2026 Imperial Valley Info-Tech LLC. All rights reserved.
IT Trends Weekly may not be reproduced, distributed, or republished in whole or in part without written permission, except for brief quotations with appropriate attribution.