

Incident Response Plan Audit Failures in 2026
Incident Response Plan audits in 2026 are exposing governance weaknesses across municipal and mid-sized organizations.
Many institutions maintain a documented incident response plan. Fewer can demonstrate that it functions operationally under audit scrutiny.
As regulatory reviews, cyber insurance renewals, and public-sector oversight increase this year, the difference between having a plan and proving it works has become measurable.
The issue is not documentation. It is operational governance.
The National Institute of Standards and Technology (NIST) emphasizes that incident response must be a structured lifecycle — preparation, detection, containment, eradication, recovery, and lessons learned — not merely a checklist document.
Similarly, the Cybersecurity and Infrastructure Security Agency (CISA) highlights that untested response procedures significantly increase operational downtime and financial impact during cyber events.
As 2026 approaches, regulatory scrutiny and insurance requirements are tightening. Organizations under 100,000 population are no longer being evaluated as “small.” They are being evaluated as “under-governed.”
Let’s examine why incident response plans fail — and how to fix them before the next audit.
Why Incident Response Plan Audits Fail in 2026
1. The Plan Exists — But It’s Not Operationalized
Auditors increasingly request:
- Evidence of tabletop exercises
- Documentation of last test date
- Named incident response roles
- Escalation workflow logs
- Communication templates
Many organizations cannot produce this.
NIST SP 800-61 Rev. 3 makes clear that incident response capability requires ongoing testing and refinement, not static documentation.
Failure mode: A PDF exists. No evidence of testing exists.
2. Roles Are Undefined or Unrealistic
In smaller organizations, IR plans frequently assign roles such as:
- “Forensics Team”
- “Legal Counsel”
- “Public Affairs Lead”
— without confirming whether those resources exist internally or under contract.
CISA notes that predefined, realistic roles are critical to reducing confusion during active response.
Failure mode: The plan references people who are unavailable or unaware.
3. No Integration with Backup & Recovery
The IBM Cost of a Data Breach Report consistently shows that tested incident response and tested backups significantly reduce breach cost and duration IBM.
Yet during audits, organizations often cannot demonstrate:
- Recovery Time Objective (RTO)
- Recovery Point Objective (RPO)
- Last full restoration test
- Backup integrity validation
An IR plan disconnected from disaster recovery is incomplete.
Failure mode: Response exists; recovery validation does not.
4. Communication Governance Is Missing
During real incidents, breakdown occurs in:
- Internal leadership notification
- Law enforcement coordination
- Public communication
- Vendor escalation
- Insurance notification timelines
CISA’s guidance emphasizes structured communications playbooks as essential to effective incident management.
Failure mode: No pre-approved communication framework.
5. The Plan Is Not Aligned to Current Threat Reality
Ransomware, supply chain compromise, SaaS data exposure, and credential theft dominate today’s landscape.
Verizon’s annual Data Breach Investigations Report (DBIR) continues to show credential misuse and ransomware as leading breach vectors Verizon.
If the IR plan still prioritizes outdated malware scenarios but does not address identity compromise and cloud exposure, auditors notice.
Failure mode: Plan does not reflect modern threat intelligence.
How to Strengthen Your Incident Response Plan for 2026 Audits
Step 1: Align to Recognized Frameworks
Use recognized frameworks such as:
- NIST SP 800-61
- NIST Cybersecurity Framework (CSF)
- CIS Critical Security Controls Center for Internet Security
Alignment demonstrates maturity and defensibility during audits.
Step 2: Conduct a Governance-Grade Tabletop Exercise
Not a casual discussion.
A structured tabletop must include:
- Scenario injection (ransomware, BEC, data exfiltration)
- Timed decision-making
- Documented outcomes
- Identified gaps
- Executive participation
Document:
- Date
- Attendees
- Lessons learned
- Remediation timeline
Auditors look for this documentation.
Step 3: Formalize Escalation & Authority
Define:
- Who declares an incident?
- Who approves shutdown of systems?
- Who contacts insurance?
- Who notifies law enforcement?
The FBI and CISA recommend early engagement with federal partners in ransomware events.
Authority confusion delays containment.
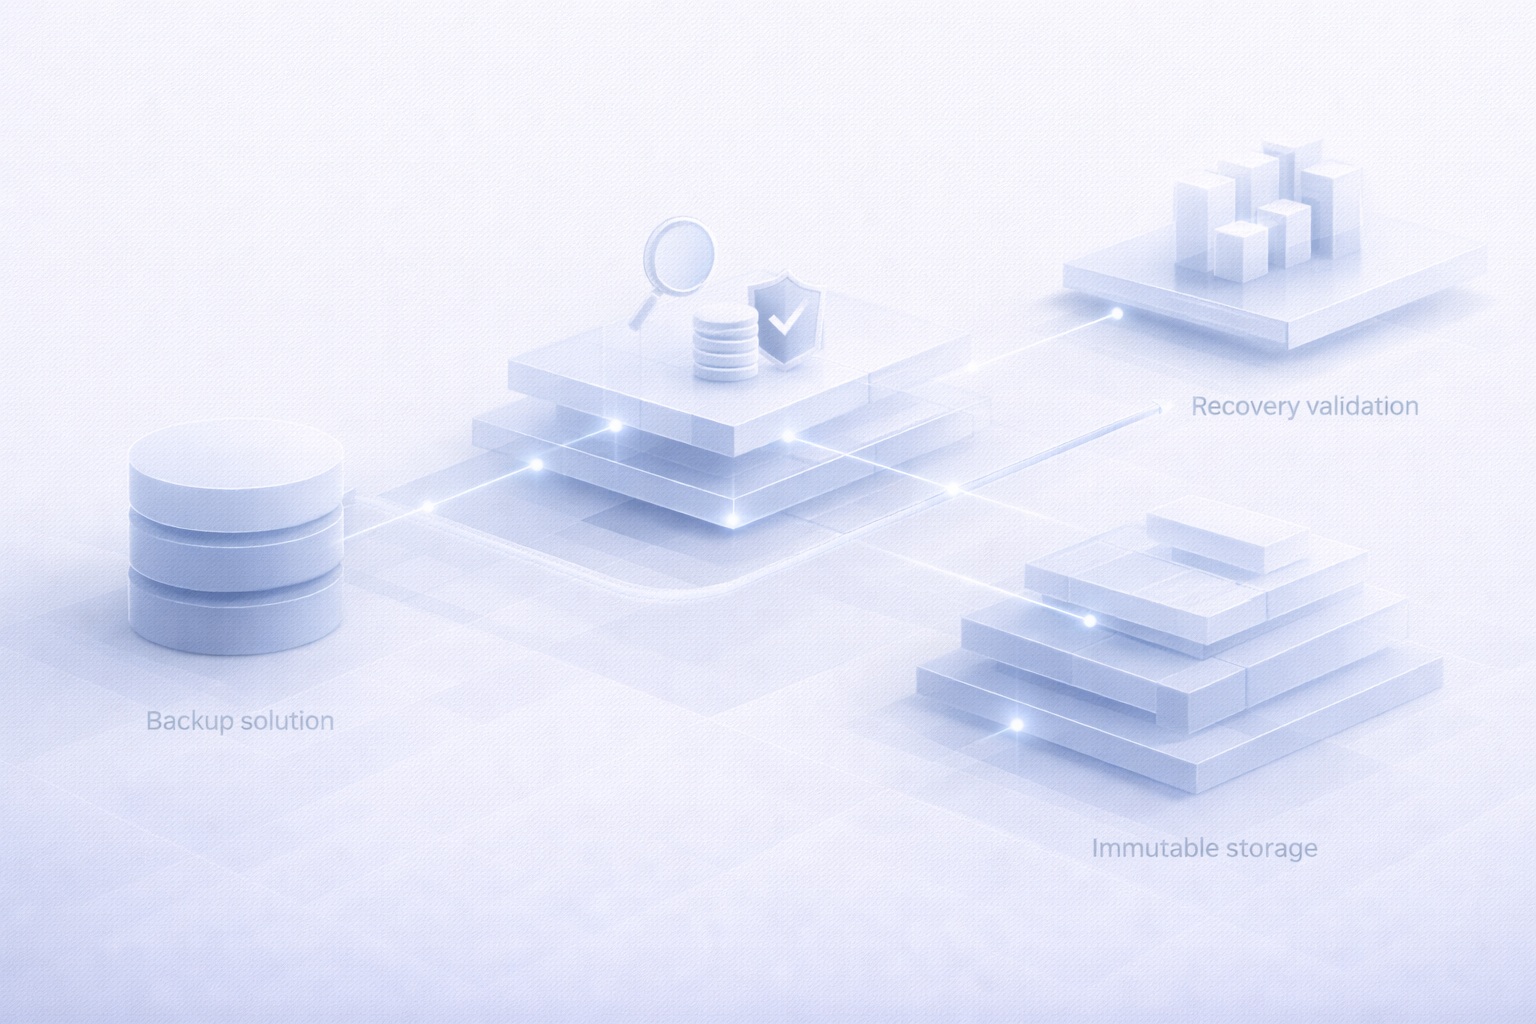
Step 4: Integrate Backup Validation
Your IR plan must explicitly reference:
- Backup architecture
- Offsite storage verification
- Restoration test frequency
- Immutable backup controls
If you cannot prove you restored from backup successfully, your IR posture is incomplete.
Step 5: Embed Insurance & Regulatory Requirements
Cyber insurance carriers now request:
- MFA enforcement evidence
- Endpoint detection logs
- Backup testing documentation
- IR plan review dates
Plans must align with underwriting expectations.
Insurance is no longer passive risk transfer. It is active governance scrutiny.
Why This Matters for Organizations Under 100,000 Population
Smaller jurisdictions and mid-sized organizations face unique risk realities:
- Limited internal IT staff
- Outsourced service providers
- Budget constraints
- Public transparency obligations
Yet ransomware actors do not scale attacks based on population size.
The FBI Internet Crime Complaint Center reports that smaller public-sector and municipal entities remain frequent targets of ransomware campaigns Federal Bureau of Investigation.
Auditors increasingly evaluate:
- Governance clarity
- Vendor oversight
- Documentation maturity
- Executive awareness
Under 100,000 population does not mean under review.
Risk Exposure During 2026 Incident Response Plan Audits
If your IR plan fails audit scrutiny, consequences may include:
- Insurance premium increases
- Coverage exclusions
- Regulatory findings
- Public reporting requirements
- Delayed recovery during real events
Governance gaps compound under stress.
Incident response must move from document compliance to operational discipline
Immediate Action Steps
- Review IR plan against NIST SP 800-61 structure.
- Conduct documented tabletop exercise within 90 days.
- Validate backup restoration.
- Update communication playbooks.
- Align plan with insurance renewal requirements.
If your organization has not conducted a governance-grade review in the last 12 months, it is overdue.
Explore our
→ Municipal IT Risk Assessment
→ Cybersecurity Governance Framework
→ Subscribe to IT Trends Weekly
→ Contact our team
Incident Response Plan Audit Documentation Checklist
During a 2026 Incident Response Plan audit, reviewers commonly request:
- Date of last tabletop exercise
- List of named response personnel
- Escalation decision tree
- Backup restoration proof
- Insurance notification procedures
- Evidence of executive review
- Third-party vendor incident clauses
- Change log of IR plan updates
If you cannot produce these within 24 hours, your governance maturity will be questioned.
Audits measure speed of documentation retrieval as much as document quality.
FAQ
Conclusion
An Incident Response Plan audit is not a paperwork exercise. It is a governance stress test.
Organizations that operationalize response reduce risk, shorten downtime, and strengthen defensibility.
Those that delay until audit day often discover their plan was theoretical.
2026 will not lower scrutiny. It will increase it.